workshop
Malware Traffic Analysis Workshop with Brad Duncan
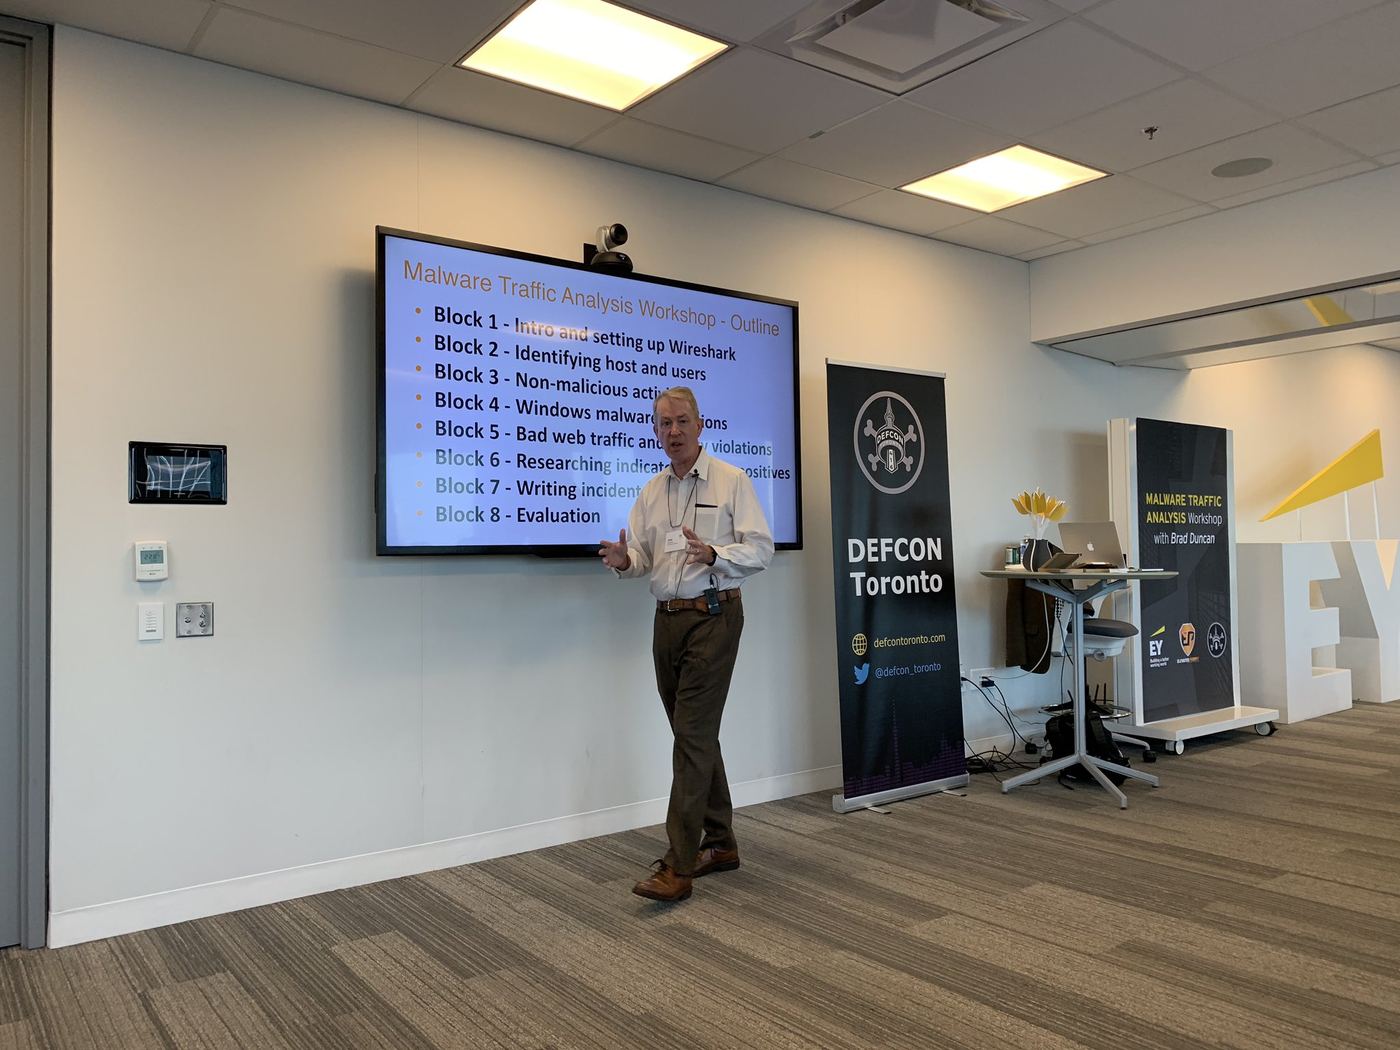
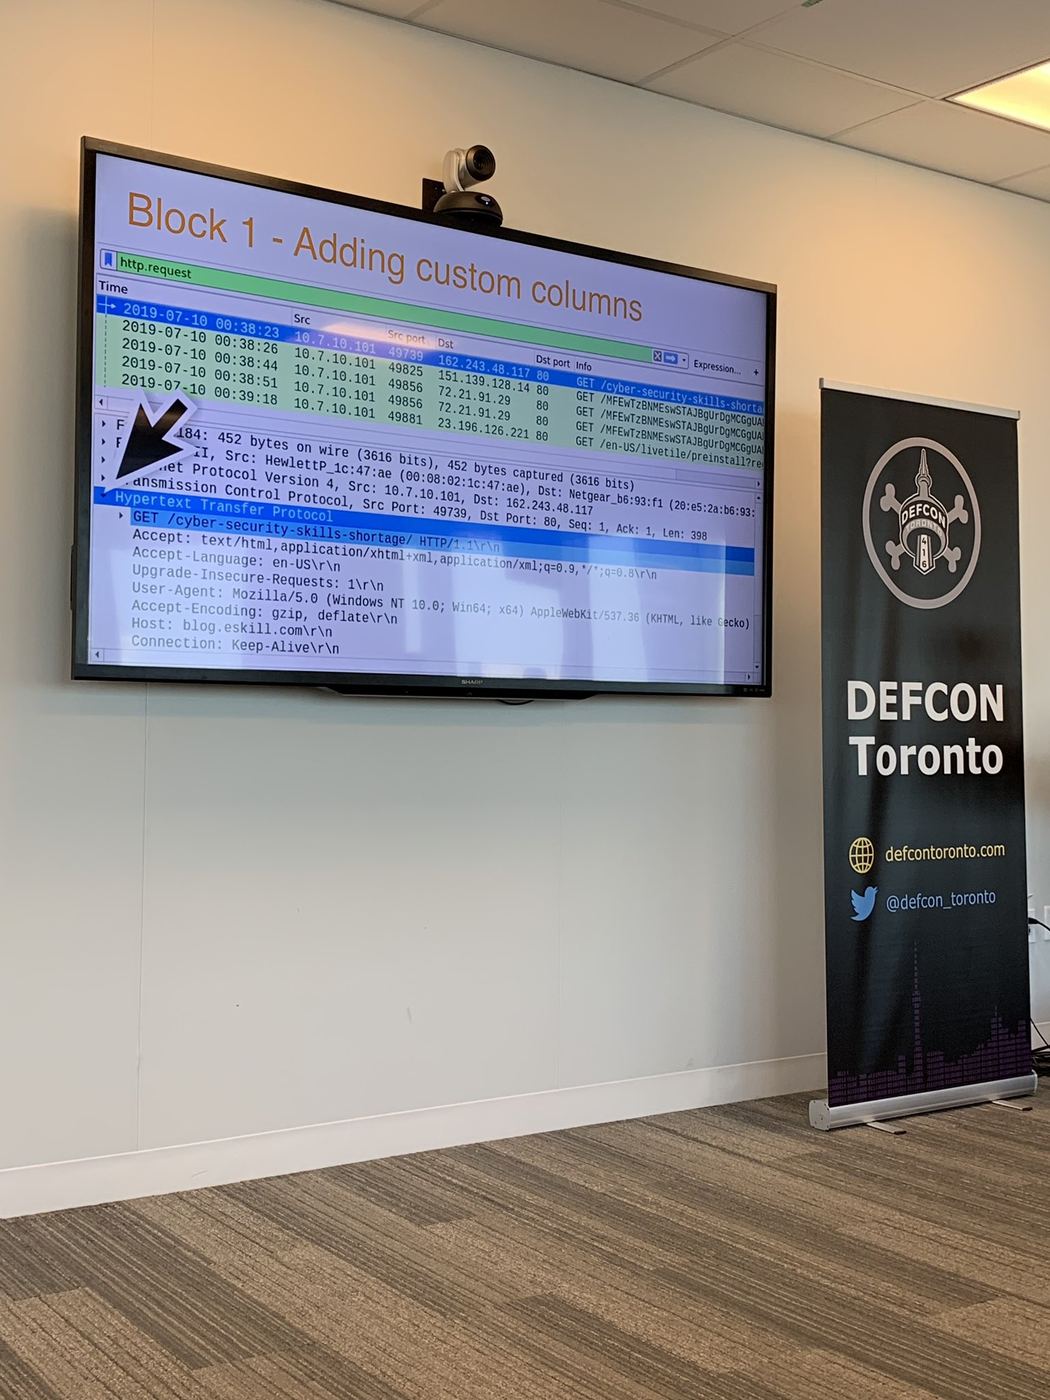
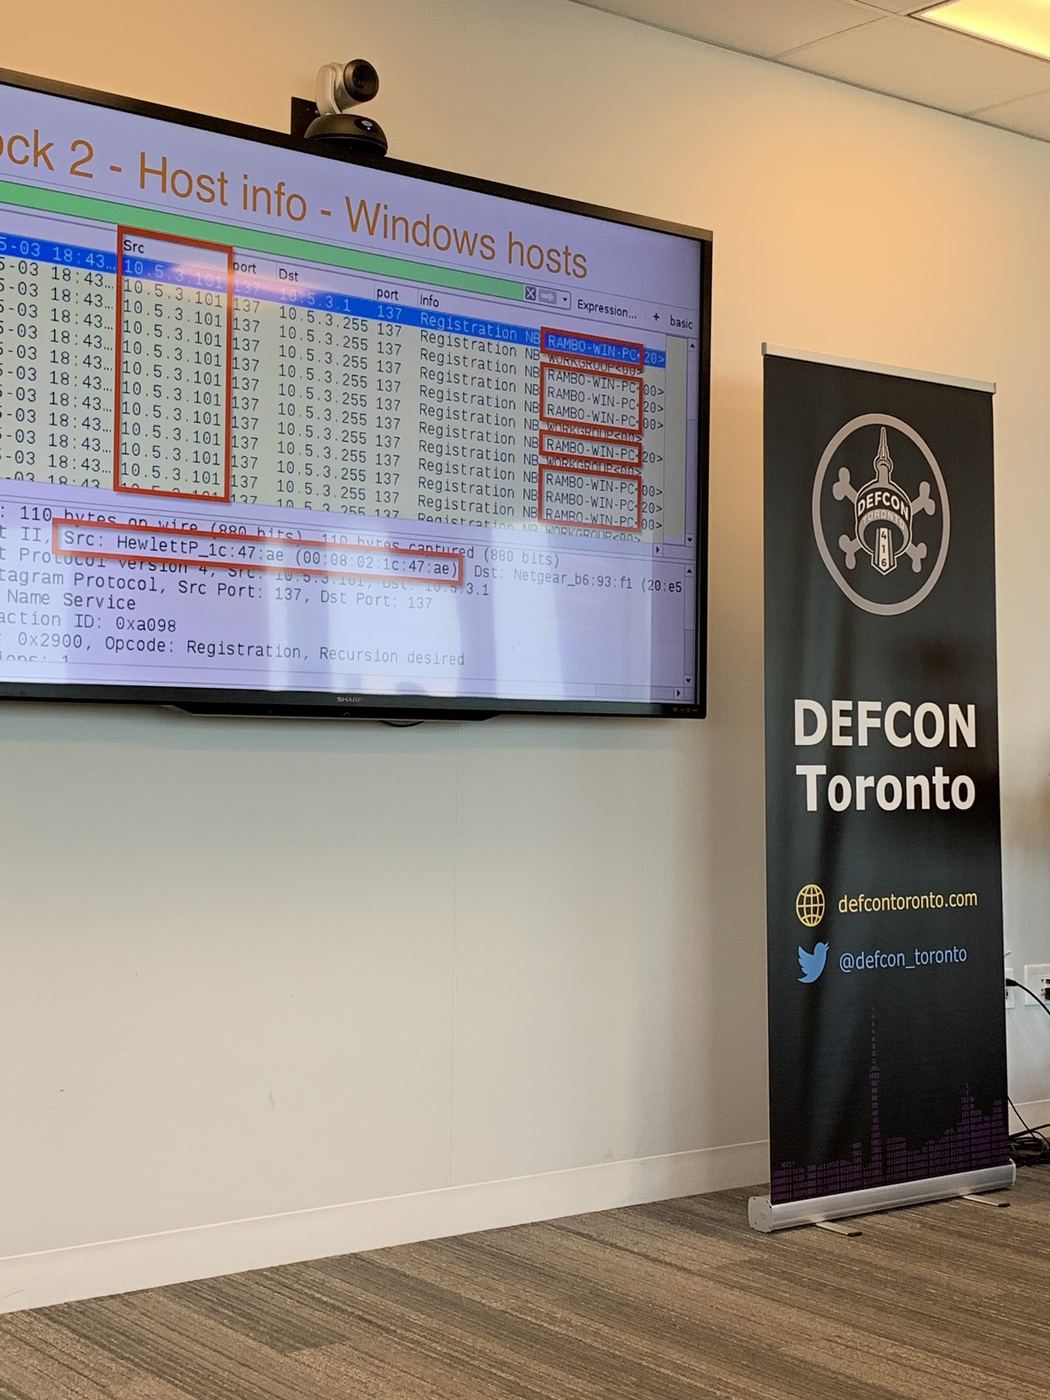
A full-day malware traffic analysis workshop at EY Tower, led by Brad Duncan, author of the Malware Traffic Analysis blog and a threat intelligence analyst at Palo Alto Networks Unit 42. The day started with basic investigation concepts and setting up Wireshark, then moved on to identifying hosts and users in packet captures of malicious traffic and recognizing what malware infections look like.
Participants worked on finding the root cause of an infection and ruling out false positive alerts. The day ended with an evaluation built around writing an incident report. EY and Elevated Prompt sponsored the workshop.
Sources & references