Hidden by Design: Battle-Tested Hybrid C2 Infrastructure
Speakers
-
Christian Ramirez
Founder and Head of Offensive Security at RBT Security. Almost two decades of pen testing, adversary simulation, malware dev, and red/purple team ops. Specializes in Objective-Based Penetration Testing. Published exploit dev on Exploit-DB as polunchis. Speaker at DEF CON, BSides, BugCON, UNAM-FES Aragón. YouTube @RBTSecurity.
-
Korenza Patterson
VP of Security Advisory and Business Development at RBT Security. Works across web, API, cloud, and mobile engagements. Translates technical red team findings into action for executives in finance, legal, healthcare, and critical infrastructure.
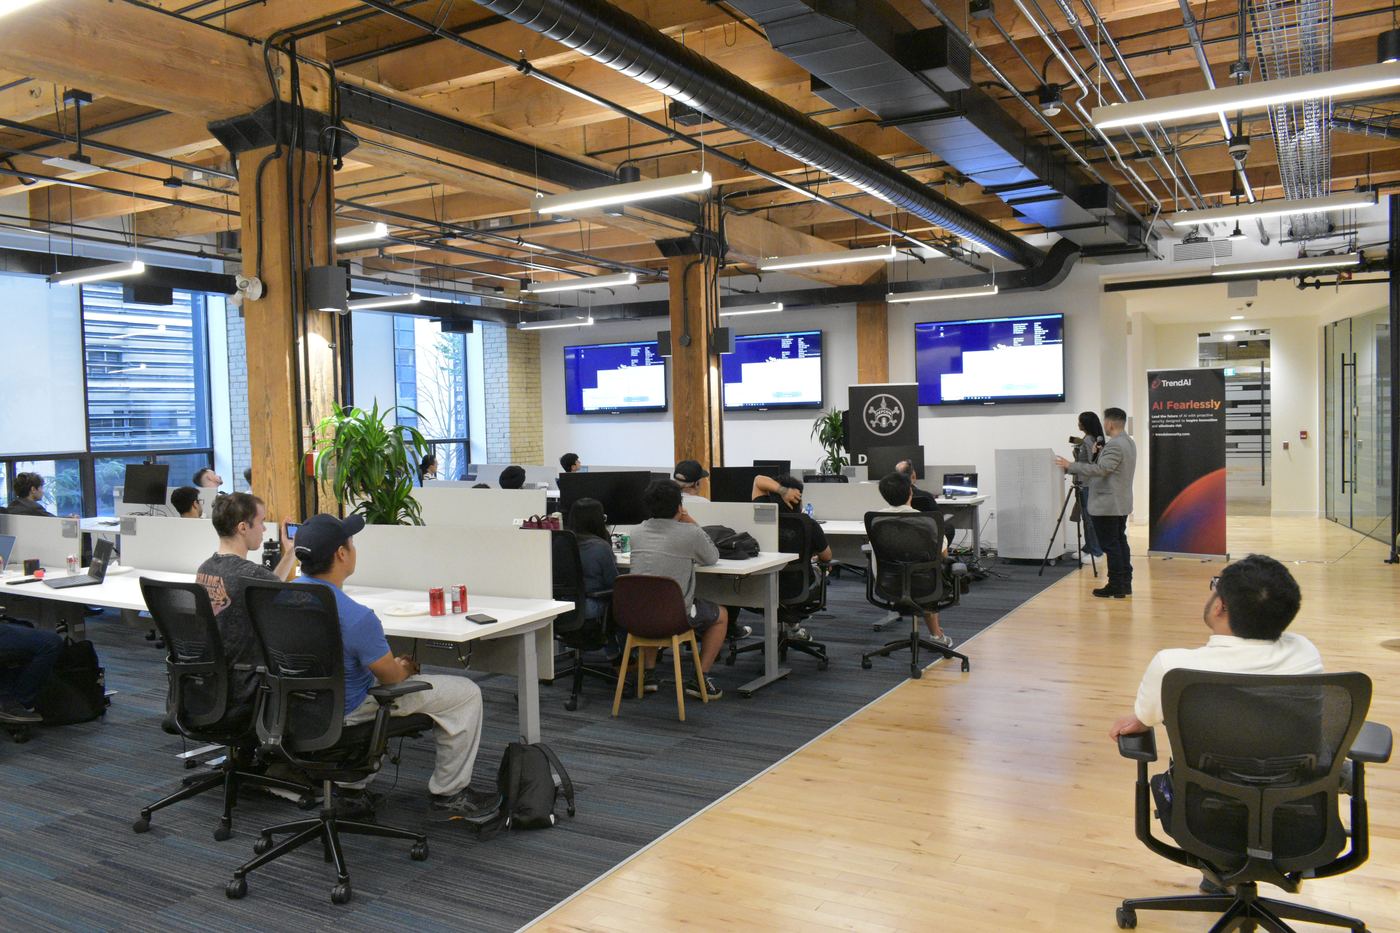
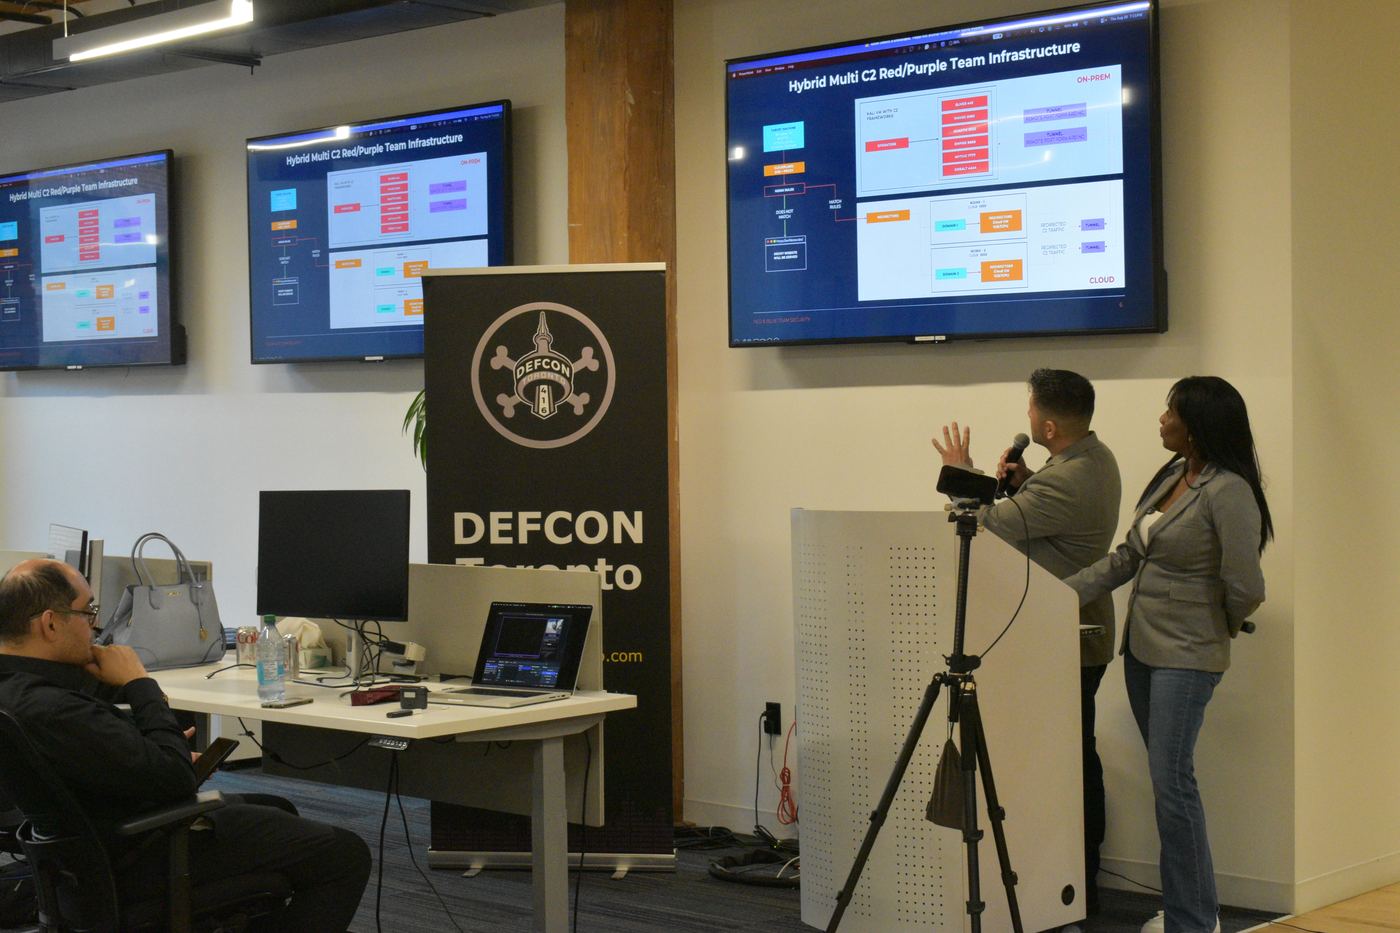
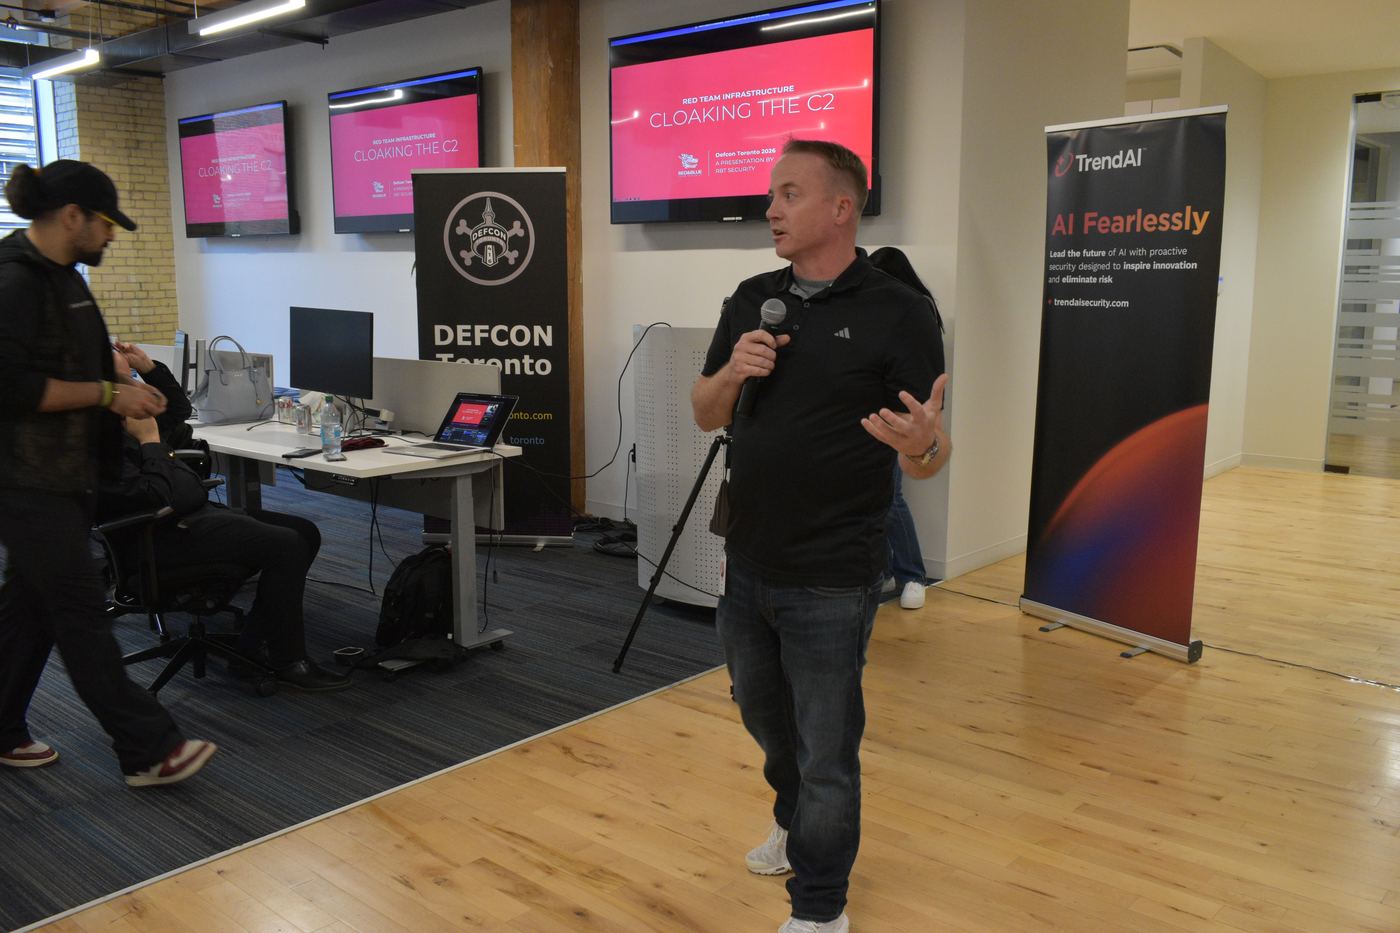
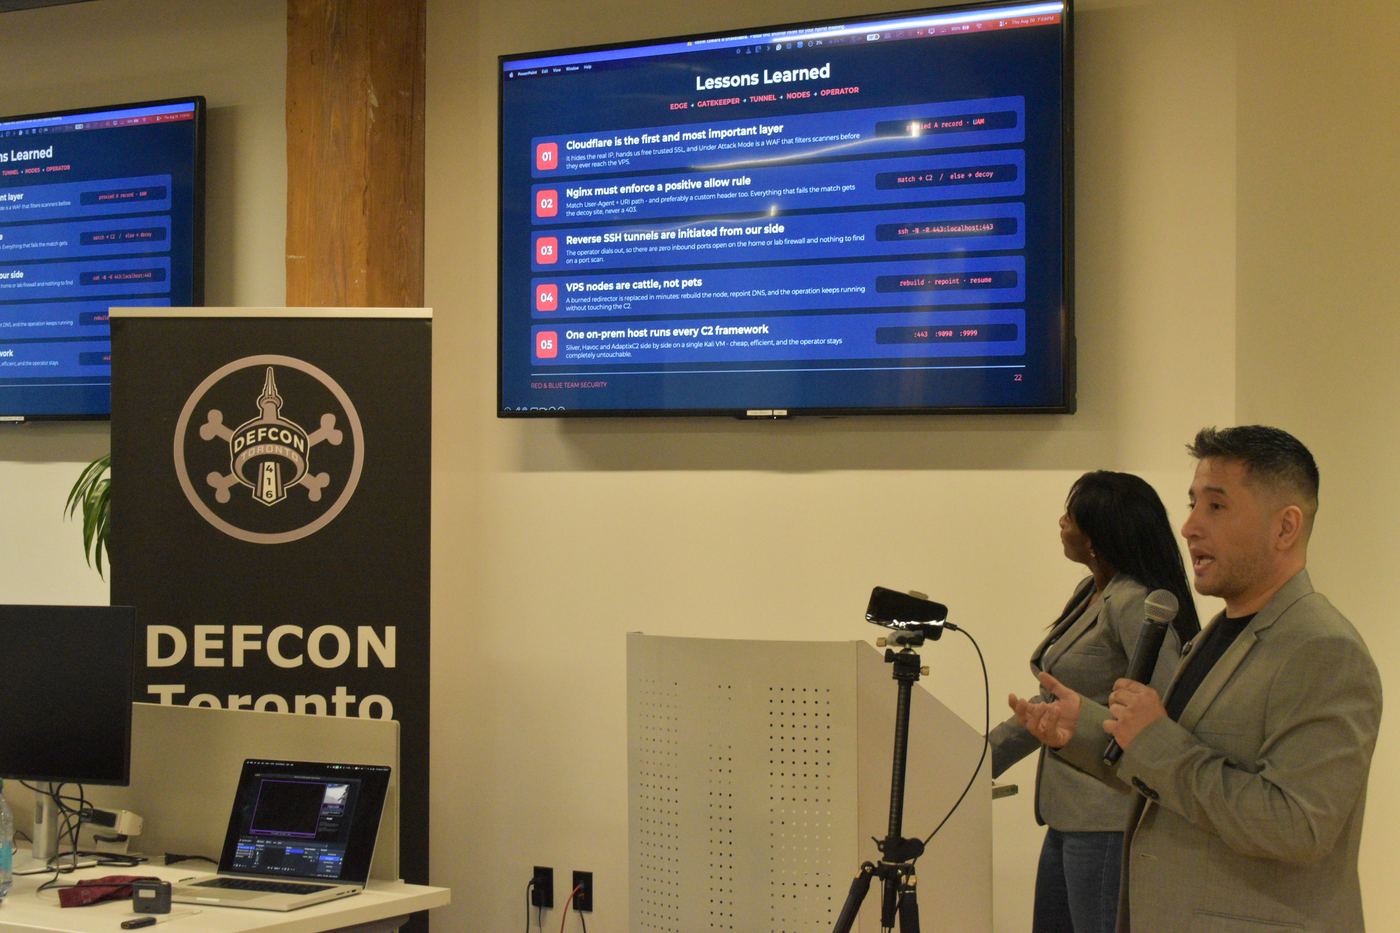
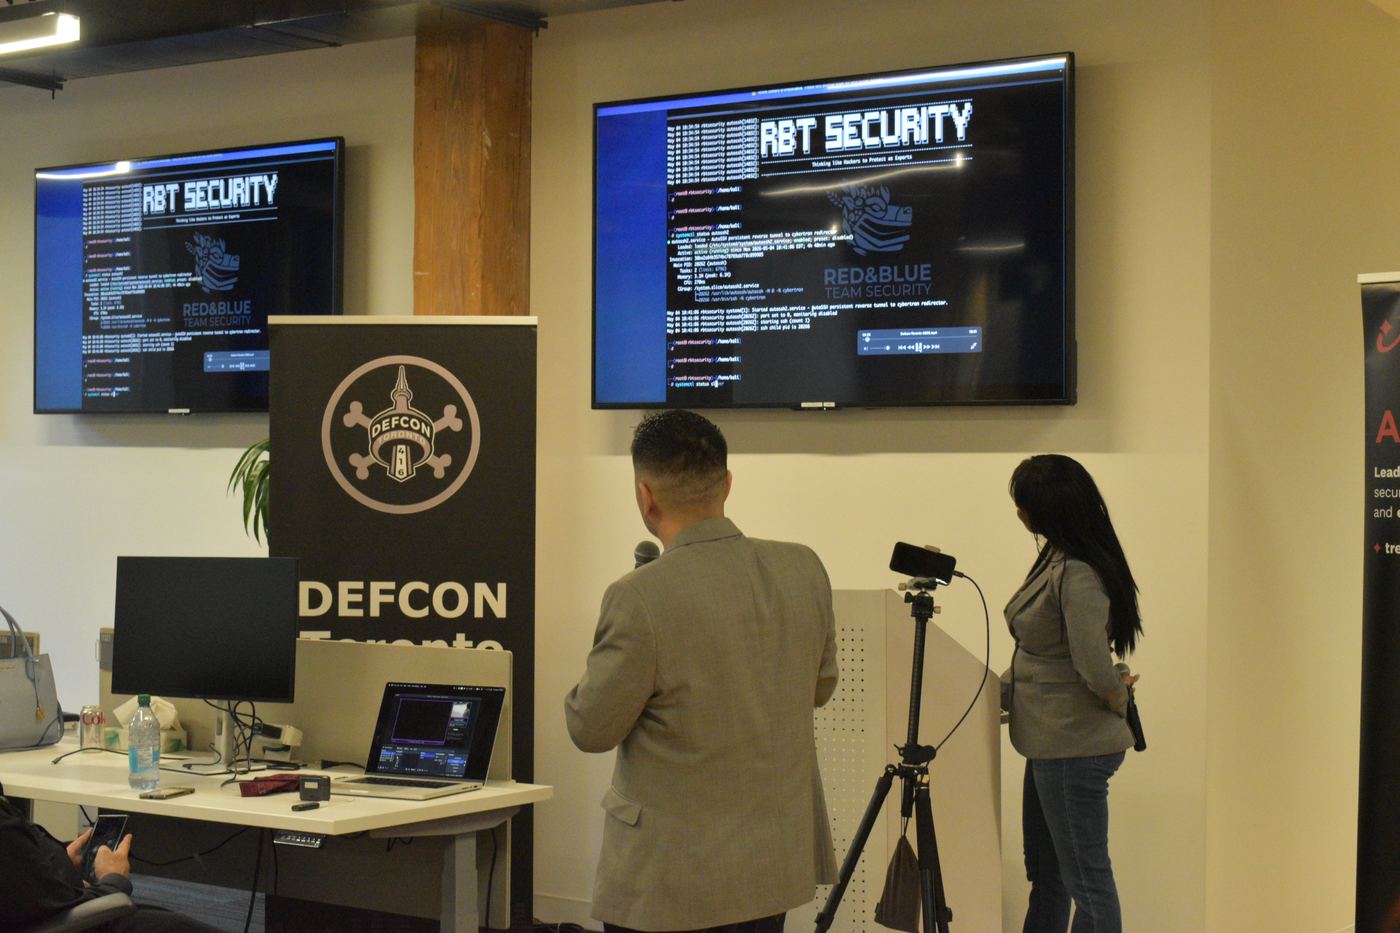
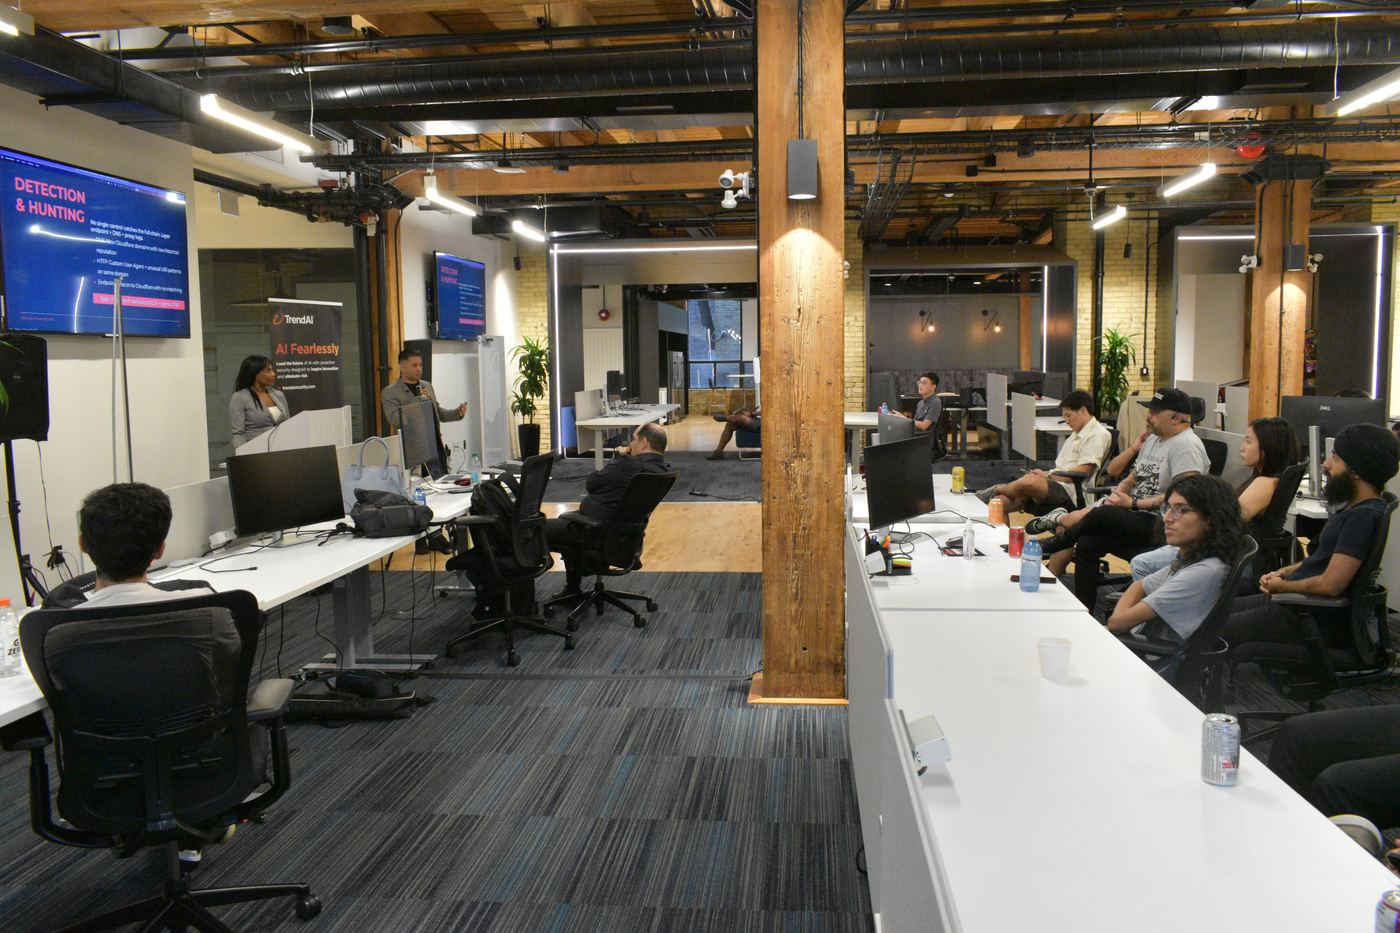
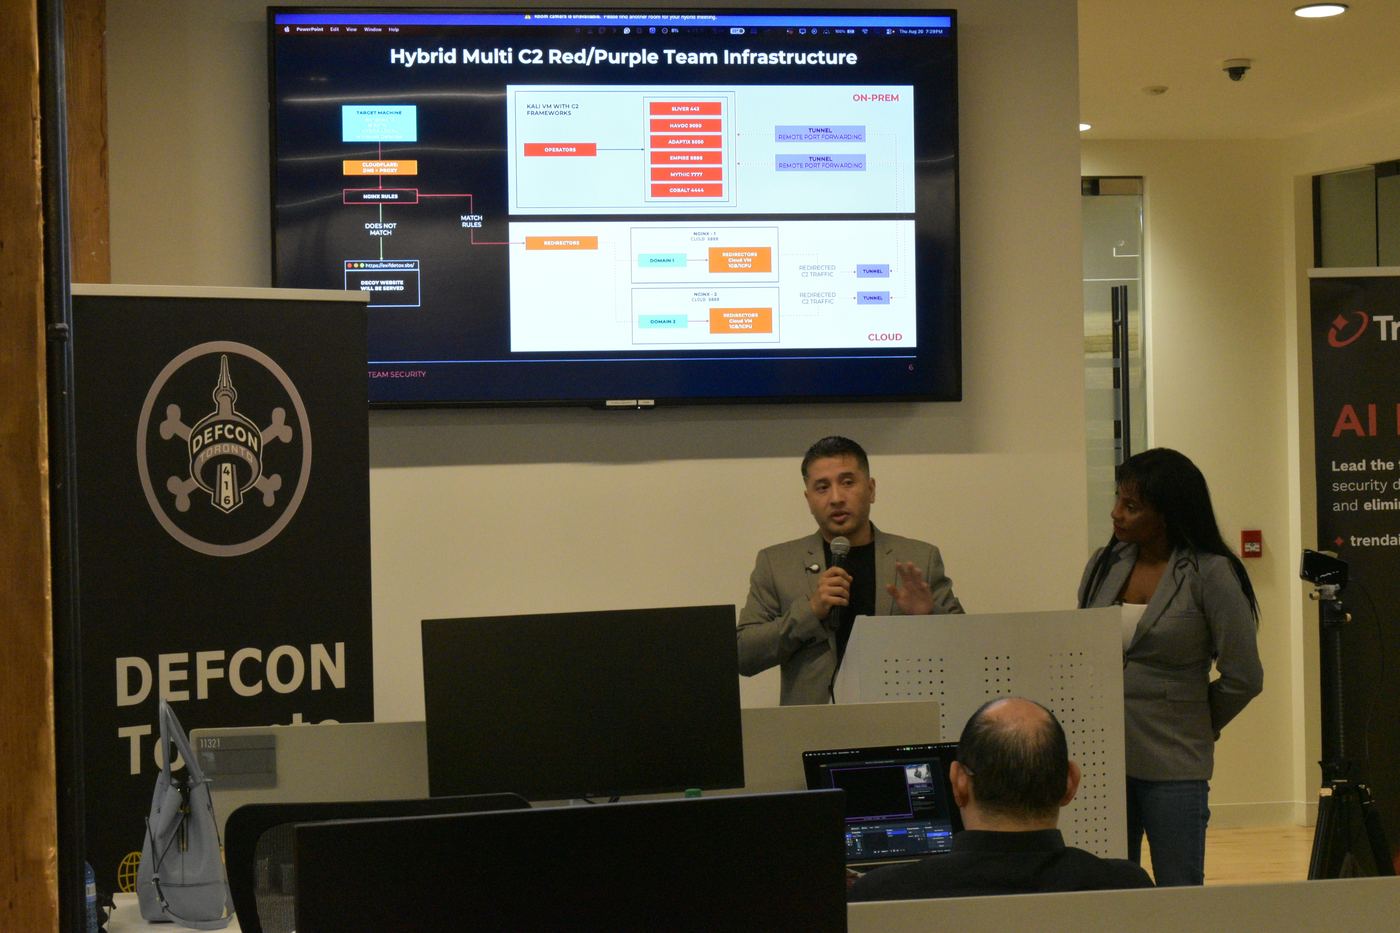
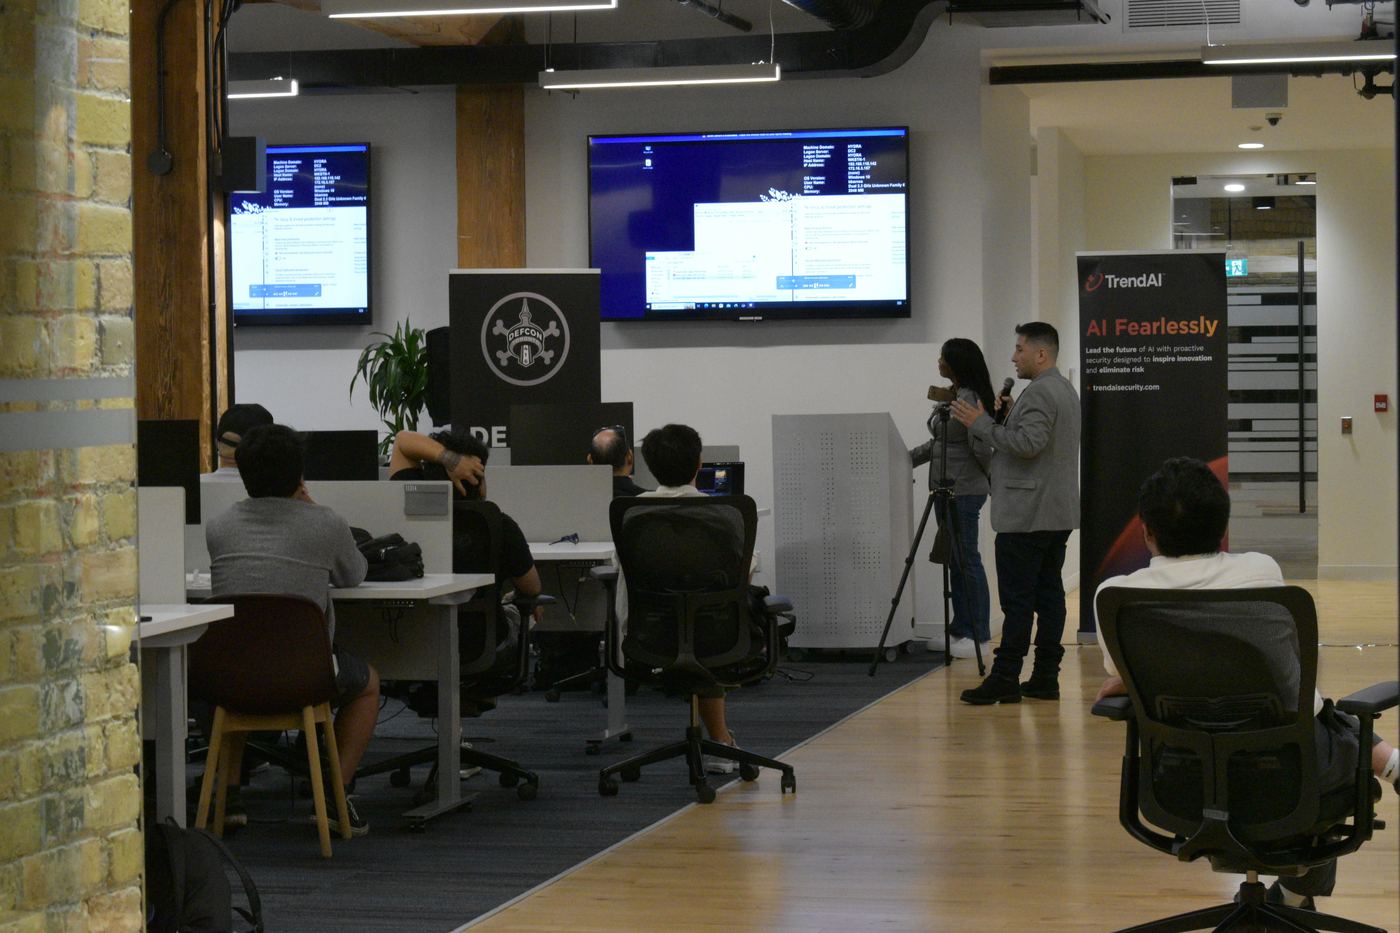
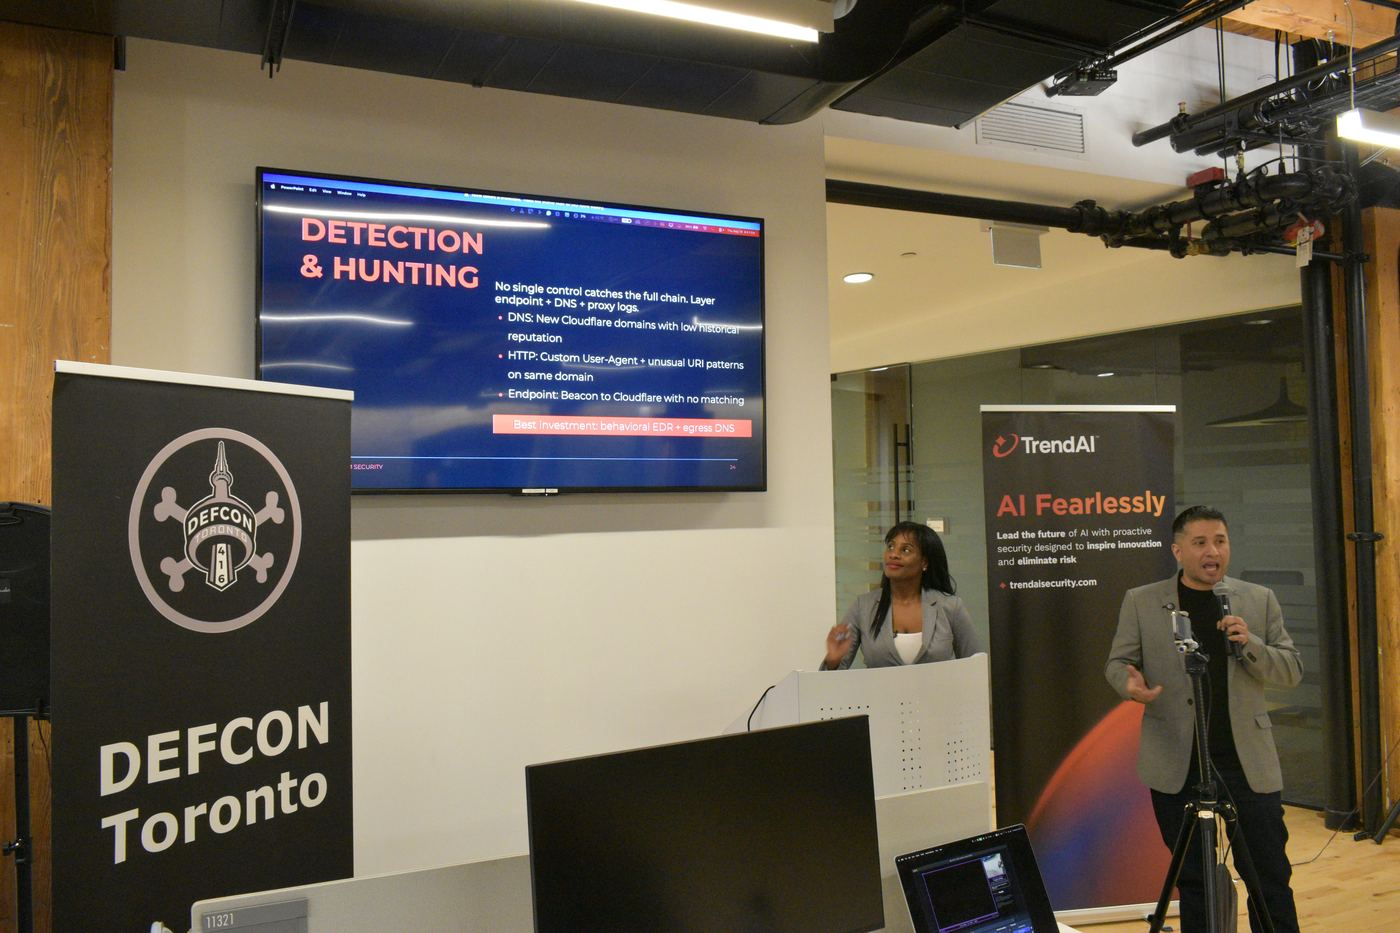
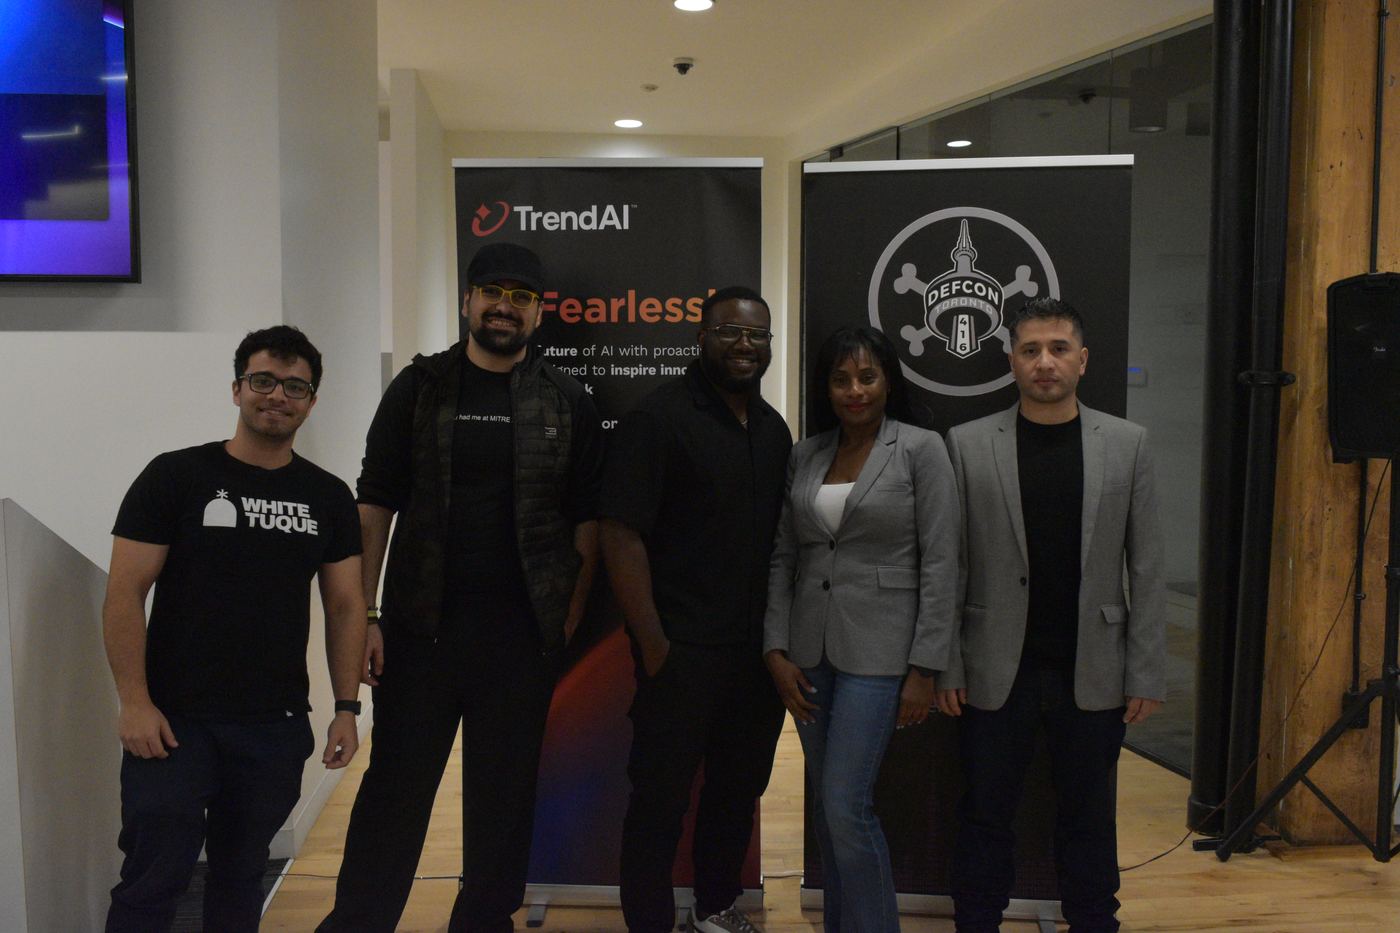
Talk night at TrendAI Toronto in Liberty Village, with TrendAI as host and sponsor. Christian Ramirez (founder and head of offensive security at RBT Security) and Korenza Patterson (VP of Security Advisory there) were the speakers, on the hybrid command and control setup RBT runs on production engagements.
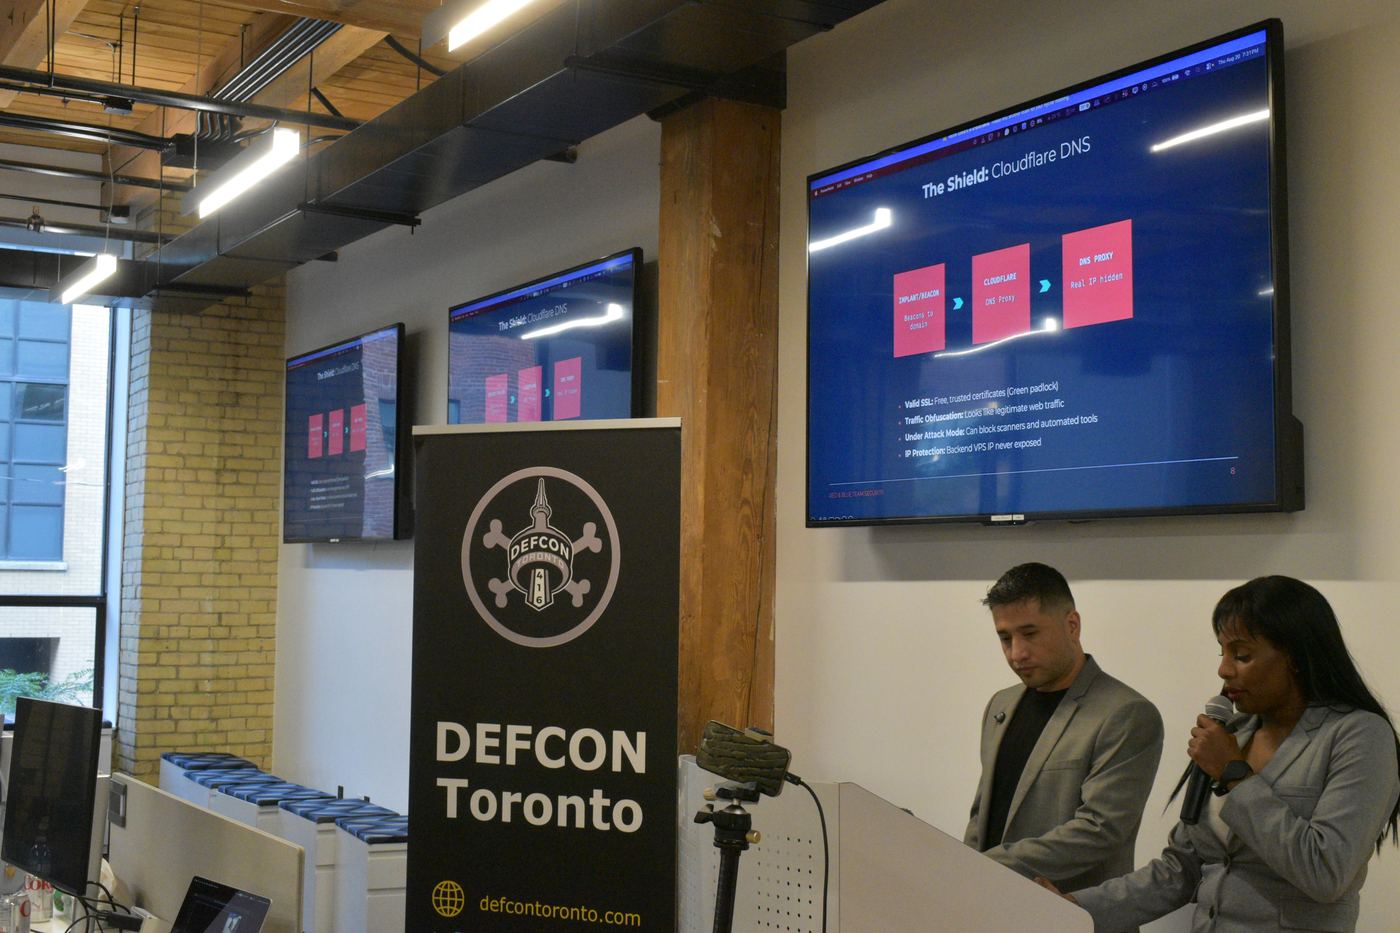
The talk was built around four areas. The first two were Cloudflare DNS proxy networks that mask backend infrastructure and Nginx redirectors that present decoy sites to defensive scanners. The other two were remote port forwarding with systemd and Auto-SSH, to bridge disposable cloud VPS assets with on-prem infrastructure, and running Sliver and Havoc/Adaptix side by side behind one cloaked network.
Sources & references
- Eventbritehttps://events.defcontoronto.ca/events